DPDP Platform RFP: A Weighted Scorecard for Choosing a Vendor
Short answer: A DPDP platform RFP is a structured request you send to vendors so you can compare DPDP compliance platforms on the same terms. A good one has three parts: requirements mapped to the DPDP Act and Rules, a weighted scorecard, and scripted demo tests. Together, they turn a sales-led comparison into an evidence-led decision.
Typically, comparison lists rank vendors by features they claim. However, claims are hard to verify, and every buyer’s needs differ. This guide gives you a DPDP platform RFP structure you can copy, a sample weighting, the demo tests that expose gaps, and the red flags to watch for. If you want a ready-made view of the market first, read our DPDP platforms comparison, then use this scorecard to test the shortlist yourself.
What is a DPDP platform RFP?
A DPDP platform RFP is a request for proposal focused on the obligations of India’s Digital Personal Data Protection Act, 2023 (DPDP Act) and the DPDP Rules, 2025. As a result, it asks each vendor the same questions, in the same format, so answers can be scored side by side.
In practice, the RFP does two jobs. First, it forces you to agree internally on what you need. Second, it also makes vendors show evidence rather than slides. As a result, the final choice is easier to defend to your board, your auditors and your DPO.
Why a DPDP platform RFP beats a feature checklist
On the one hand, feature checklists reward vendors that tick every box. By contrast, an RFP with weights rewards the features that matter to you. For example, a hospital may weight children’s and health data highly. Meanwhile, a SaaS company may weight processor management and cross-border questions instead.
In addition, the DPDP Act puts the burden of proof on you. Section 6(10) says the Data Fiduciary must prove that notice was given and consent was obtained. Therefore, evidence features, such as consent records and audit logs, deserve real weight in any DPDP platform RFP.
How a DPDP platform RFP works: the five sections
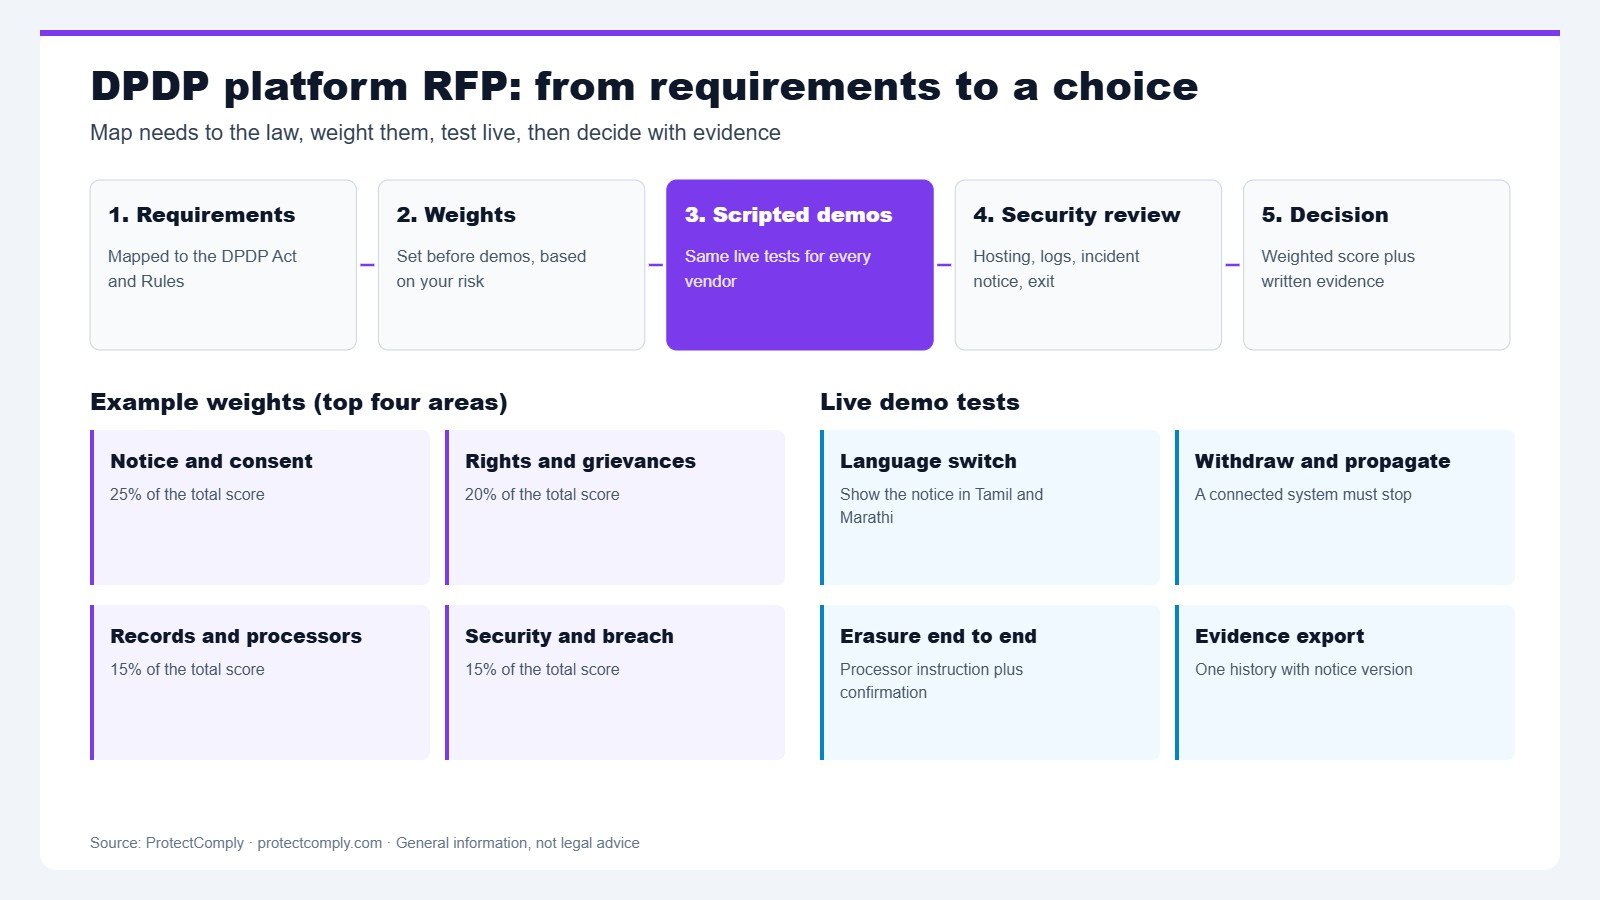
We suggest organising the DPDP platform RFP into five sections. In turn, each one maps to obligations in the Act or Rules.
- Notice and consent. Can the platform produce a Rule 3 notice that is standalone, clear and itemised? Can it offer English and all 22 Eighth Schedule languages, as Sections 5(3) and 6(3) require? Similarly, does withdrawal work as easily as consent, under Section 6(4)?
- Rights and grievances. Does it handle access, correction, erasure and nomination requests? Also, does it track the ninety-day grievance limit in Rule 14?
- Records and processors. Does it maintain a record of processing, a processor register and erasure instructions to processors, as Section 8(7)(b) requires?
- Security and breach. Does it support the Rule 6 safeguards, including logs kept for at least one year? In addition, can it run a breach workflow that meets the Rule 7 report within 72 hours?
- Evidence and audit. Can you export consent records, notice versions and audit logs for the Data Protection Board?
A sample weighted scorecard
The weights below are an example, not a standard. Therefore, adjust them to your sector and risk profile. Next, score each vendor from 0 to 5 on each line, and multiply by the weight.
| Area | Example weight |
|---|---|
| Notice and consent | 25% |
| Rights and grievances | 20% |
| Records and processors | 15% |
| Security and breach | 15% |
| Evidence and audit | 15% |
| Commercials and support | 10% |
For this reason, keep the scoring rules written down before demos start. Otherwise, the loudest demo tends to win. Also, ask two people to score separately, then compare.
A practical example
For example, a mid-sized NBFC shortlists three vendors. It weights notice and consent at 25% and security at 20%, because it serves many first-time borrowers and handles financial data. At first, Vendor A demos well but cannot show notice versions in consent records. In contrast, Vendor B scores lower on design but exports complete evidence. As a result, Vendor B wins on the weighted score, and the DPO can explain why.
Scripted demo tests for your DPDP platform RFP
First, ask every vendor to run the same live tests. Also, do not accept pre-recorded demos for these.
- Language switch. Show a notice, then switch it to Tamil and Marathi.
- Withdraw and propagate. Withdraw a test consent and show that a connected system stops processing.
- Erasure end to end. Approve an erasure request, then show the processor instruction and its confirmation.
- Breach clock. Open a test incident and show the 72-hour timer and report output.
- Evidence export. Export one person’s consent history, including the notice version they saw.
In practice, these tests reveal more than any datasheet. Propagation and evidence export are the likeliest places for gaps, because they depend on integrations rather than the interface.
Sample questions for each DPDP platform RFP section
To begin with, use short, testable questions. Moreover, ask vendors to answer “yes, show me” or “no”, with evidence for every yes.
- Notice and consent: Can we version notices and see which version each person saw? Also, can one person hold different consents for different purposes?
- Withdrawal: Is withdrawal available in the same place and language as consent? Moreover, does it reach connected systems automatically?
- Rights: Can people submit requests through a public portal? Also, does the system track due dates and reasons for refusal?
- Processors: Can we record every processor and send erasure instructions to them? Then, do we get confirmations back?
- Security: Where is our data hosted, including backups? Also, how fast will you tell us about an incident?
- Evidence: Can we export all records in a standard format, both during the contract and at exit?
- Commercials: What does pricing depend on, such as records, users or modules? Finally, what does implementation include?
Finally, keep each vendor’s written answers with your scorecard. Together, they form the audit trail for your DPDP platform RFP.
Comparing ways to run the selection
| Method | Main benefit | Main risk |
|---|---|---|
| Published “top 10” lists | Fast longlist | Rankings may favour the author |
| Feature checklist | Simple to run | Every vendor ticks every box |
| Weighted DPDP platform RFP | Defensible, evidence-led choice | Takes a few weeks |
Pros and cons of a formal DPDP platform RFP
Pros:
- Above all, every vendor answers the same questions.
- Weights reflect your risks, not the vendor’s pitch.
- The decision is documented for audit and board review.
Cons:
- Firstly, it takes time to write and run.
- Similarly, smaller teams may find full scoring heavy.
- A strong score does not guarantee compliance. Your own processes still matter.
Red flags in vendor answers
- “Fully DPDP compliant out of the box”. No tool can make a business compliant on its own.
- Vague language support. “Multilingual” without naming all 22 Eighth Schedule languages.
- No processor erasure. In other words, the platform stops at your own systems.
- Wrong dates. Any claim that differs from the 13 May 2027 commencement of the core obligations deserves a follow-up question.
- No evidence export. As a result, you cannot get your records out in a usable format.
How we measure success
These indicators show whether your DPDP platform RFP worked. We do not publish benchmark figures for them.
- Requirement coverage: the share of RFP lines the chosen platform met in live tests.
- Score agreement: how closely independent scorers agreed.
- Time to first evidence: the time from contract to your first complete consent export.
- Post-launch gaps: the number of requirements found missing after go-live.
Frequently asked questions
How many vendors should a DPDP platform RFP include?
Three to five is usually enough. After all, fewer limits comparison, while more makes scoring slow.
Should consent managers be treated differently?
Yes. A Consent Manager under Section 6(9) must register with the Data Protection Board. Rule 4, on registration, commences on 13 November 2026. If a vendor claims to be a Consent Manager, ask for its registration status.
What weight should security get?
It depends on your data. For instance, for financial or health data, many buyers weight security and breach handling at 20% or more.
Can we reuse our ISO 27001 vendor questionnaire?
Partly. Although it covers security well, it will not test notices, consent, rights or processor erasure. Add DPDP-specific sections.
Do we need legal review of the RFP?
It helps, because legal or privacy review makes sure the requirements match your actual obligations.
When must the platform be ready?
The core DPDP obligations commence on 13 May 2027. So allow time for set-up, integrations and testing before that date.
Summary and next step
In summary, a DPDP platform RFP gives you a fair, evidence-led way to choose a vendor. Map requirements to the law, weight them to your risks, run scripted demo tests, and watch for red flags. Finally, document the decision for your DPO and auditors.
Naturally, we welcome being tested this way. Review ProtectComply’s features against your scorecard, see the product modules, or book a scripted demo using the tests above.
Published by Jupinder Singh Bedi, CEO and Co-Founder, ProtectComply. SEO: Yatin Chaudhary. Legal references: Digital Personal Data Protection Act, 2023, Sections 5(3), 6(3), 6(4), 6(9), 6(10) and 8(7); Digital Personal Data Protection Rules, 2025, Rules 1, 3, 4, 6, 7 and 14. This article is general information, not legal advice.